

Puppet Enterprise flaw is under attack: patch the server now
Puppet Enterprise flaw is under attack; update Puppet Server to 2026.0.1, 2025.12.1 or 2023.8.13
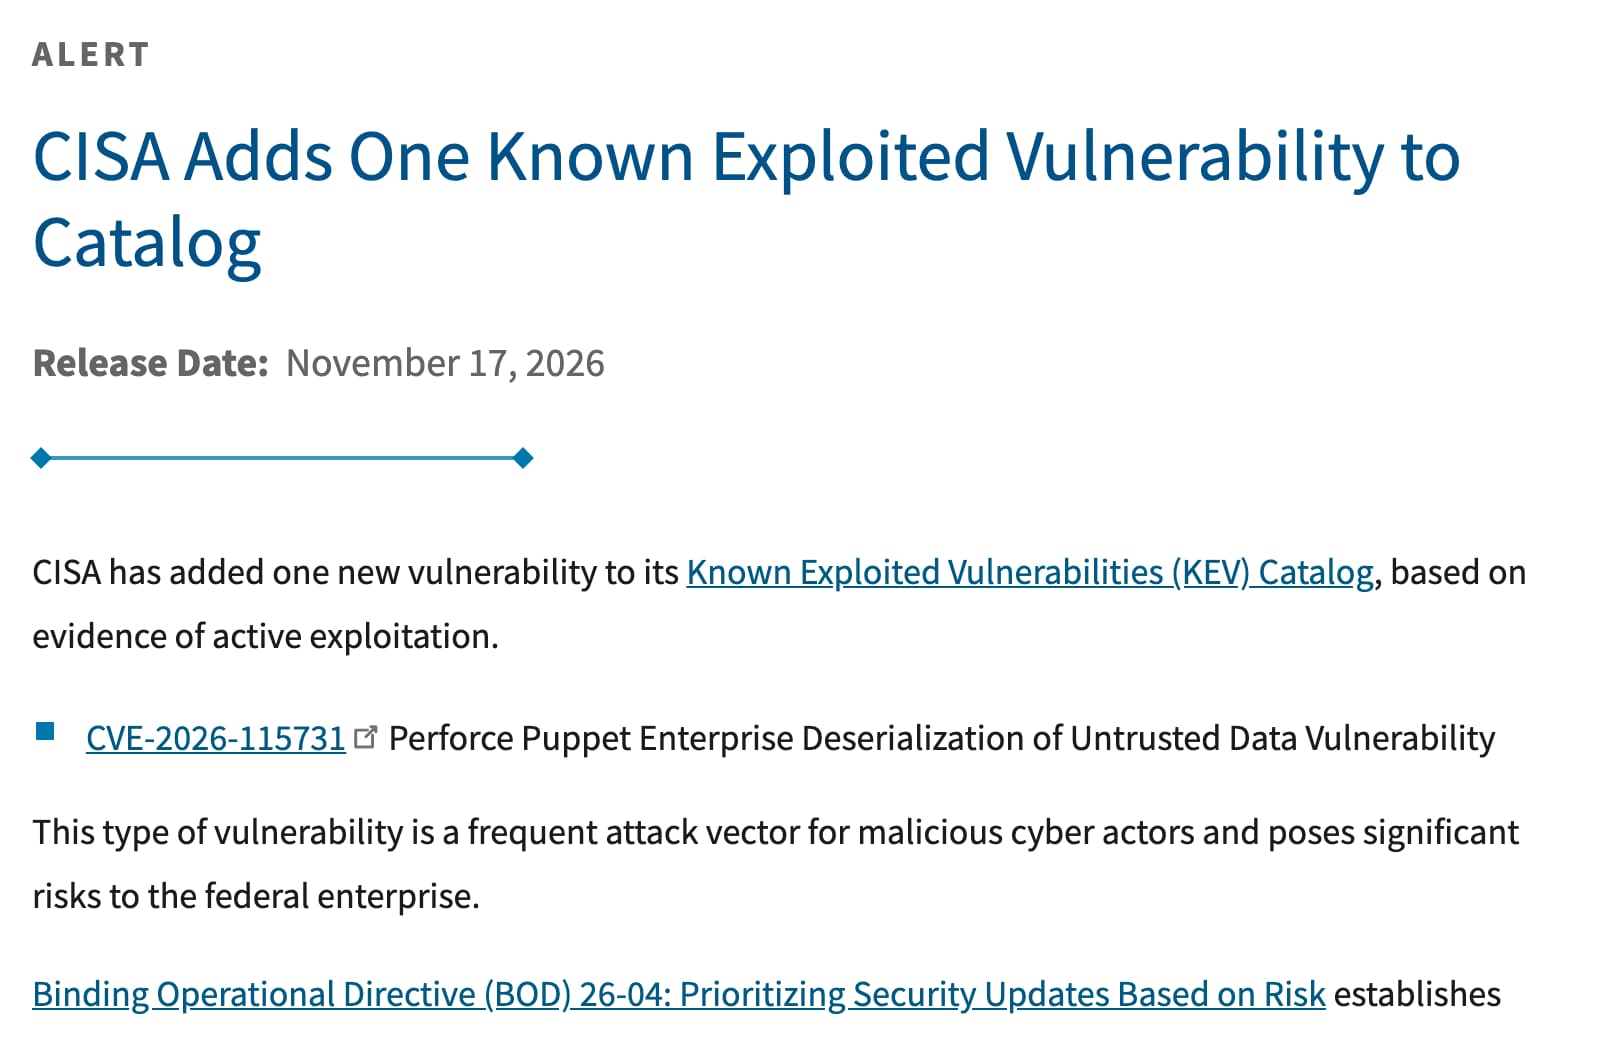
Attackers are exploiting CVE-2026-115731, a critical flaw in the server software behind Puppet Enterprise, the tool IT teams use to manage many computers from one place. The flaw lets someone on the network run their own code on the server, and the risk is highest where the server signs new certificates automatically. CISA added it to its list of flaws in active use on 17 November, and Perforce has released fixed versions.
What to do this week
- Update Puppet Enterprise to a fixed version.Use 2026.0.1 or later on the 2026 line, 2025.12.1 or later on 2025, and 2023.8.13 or later on 2023. Then restart Puppet Server, because the fix only loads on restart.
- If you cannot update today, stop automatic signing.Review the autosign setting and turn it off, or require checks on each new certificate request. Help Net Security names this as the temporary step.
- Check the list of signed certificates.Look for any machine you do not recognise. An unknown machine holding a valid certificate needs a closer look before anything else.
- Look for unusual activity on the server.Check for unexpected processes, files or outgoing connections tied to the Puppet Server account. If you find any, patching is not enough. Help Net Security advises treating the certificate authority as compromised and rebuilding it.
- Limit who can reach port 8140.Only the computers you manage should be able to reach the Puppet server on that port. Block it from the wider network and from the internet.
What happened
Attackers are exploiting a serious flaw in Puppet Enterprise, the software many IT teams use to set up and manage computers from one central server. The US cybersecurity agency, CISA, added the flaw on 17 November to its list of bugs known to be used in real attacks. CISA said it acted on evidence of active exploitation[1]. Perforce, the company behind Puppet, has released fixed versions.
The flaw is tracked as CVE-2026-115731. It sits in the part of Puppet Server that takes in reports from each managed computer after a run. The server unpacks a report without checking it properly, so a crafted report can make it run the sender's code, with the rights of the Puppet service account. Help Net Security[2] describes it as a remote code execution flaw, which means someone on the network can run code on the server without any login to it.
Who can send that report matters. A computer must hold a certificate signed by the Puppet certificate authority (CA), the part of the server that vouches for each machine. Where the CA signs new requests automatically, without checking them, an outsider on the network can get a certificate and then use the flaw. Every source rates it critical.
- Severity
- Critical
- In use
- Yes. CISA cites evidence of active exploitation and added the flaw to its Known Exploited Vulnerabilities list on 17 November.
- Fixed in
- Puppet Enterprise 2026.0.1, 2025.12.1 and 2023.8.13, depending on the version you run.
- Federal deadline
- 1 December 2026 for US federal agencies, according to Help Net Security.
The full story1 more section
Who is affected
Anyone who runs Puppet Enterprise or Puppet Server, and anyone who runs OpenVox Server, the open-source fork of Puppet. Families are unlikely to run this themselves. It matters to the IT provider, school, or business whose management server runs Puppet.
The greatest exposure is a server that signs certificates automatically and can be reached from networks you do not control. Puppet Server listens on port 8140 by default. It also reports a second flaw, CVE-2026-115732, that lets one machine pose as another, which Perforce has also fixed.
Timeline
-
HARD publishes its article, at High.
After the news
- How to update every device phones, computers, browsers, TVs and routers
References3
- ^ CISA (). “CISA Adds One Known Exploited Vulnerability to Catalog”. Adds CVE-2026-115731 to the KEV catalog based on evidence of active exploitation; describes the deserialization flaw.
- ^ Help Net Security (). “Exploited Puppet flaw puts the server that configures your endpoint fleet at risk (CVE-2026-115731)”. Affected and fixed versions, autosign condition, temporary mitigation, detection steps, federal deadline, CVE-2026-115732.
- The Hacker News (). “Hackers Exploiting Critical Puppet RCE Flaw Affecting Enterprise Management Servers”. Reports CVSS 9.4 and the CISA KEV addition. Full article returned an error; read from its feed summary only.
Situation Room articles are updated as events develop: updates are added to the timeline, and never edited away. Follow them by email or RSS.