

Northflank, a platform-as-a-service, is the ninth developer platform this month to lose the keys customers stored with it
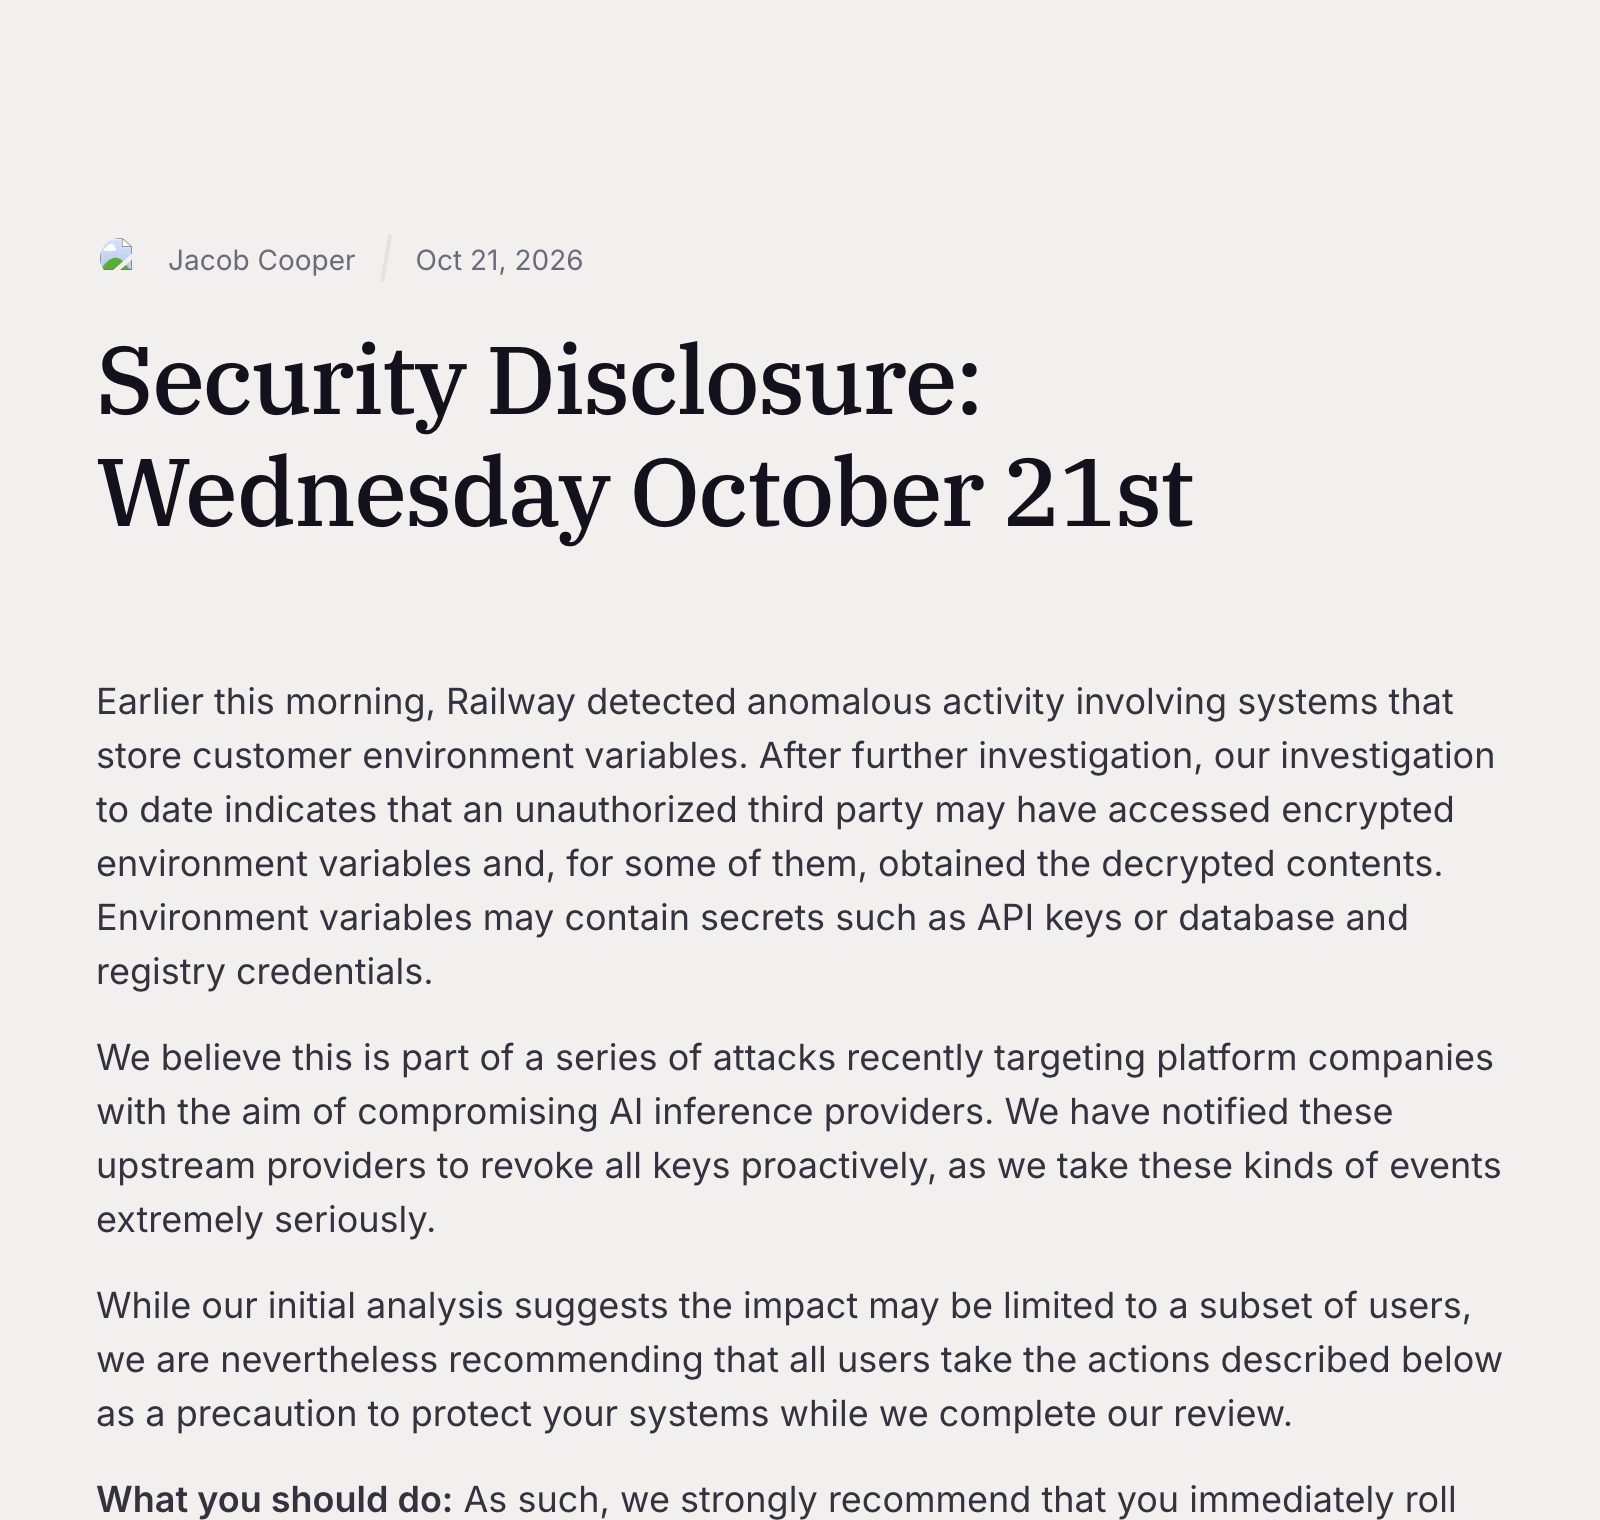
Railway, a hosting platform popular with developers, says someone accessed the secrets customers store with it, some decrypted. It believes it's part of a series of attacks on platforms, aimed at AI providers, after Fireworks AI and OpenCode.
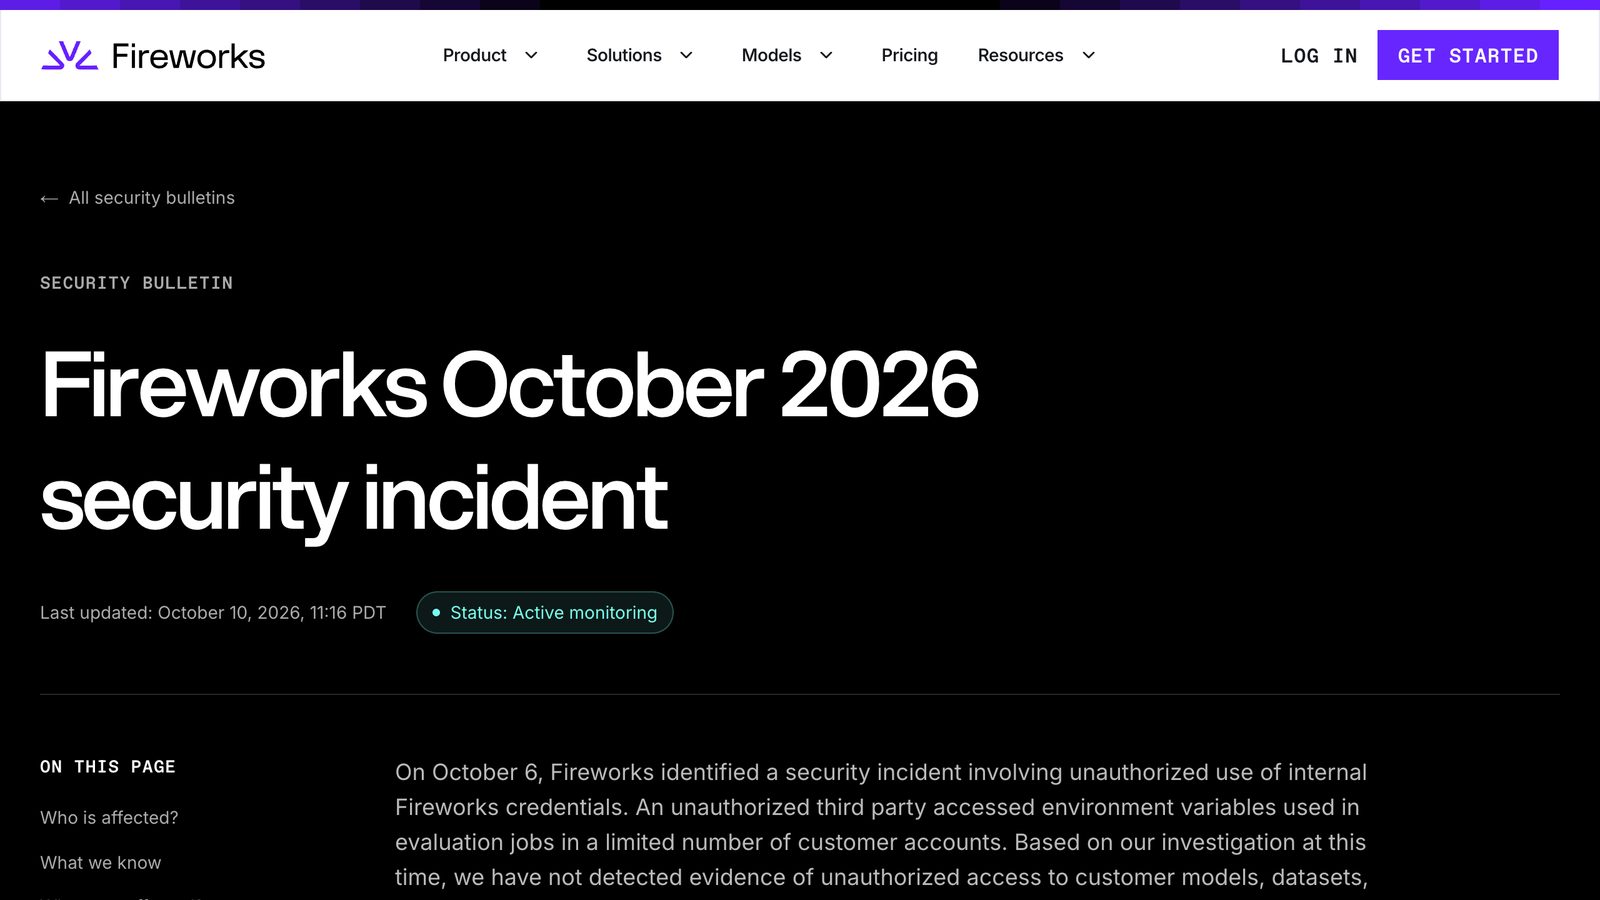
Fireworks AI, OpenCode and now Railway. Three platforms in fifteen days, each breached for the same kind of thing: the keys their customers trusted them to hold.
What happened
On Wednesday, Railway, a hosting platform popular with software developers, told its customers that someone had been inside the systems where it keeps their secrets. Not their websites, their secrets: the passwords, database logins and API keys their software uses to talk to everything else. For some customers, the attacker got those secrets in plain text.
Railway paused every deployment on its platform, asked AI companies upstream to cancel keys, and told every customer to change every secret they'd stored with it. Then it said the part that matters most: it believes this is one of a series of recent attacks on platform companies, aimed at getting into AI providers.[1]
Fifteen days, three platforms: Fireworks AI, then OpenCode, then Railway. Fireworks and OpenCode haven't said whether their breaches are connected.
Timeline
-
Fireworks AI. [2]
- Taken
- API keys and tokens customers stored for evaluation jobs
- How
- Stolen internal Fireworks credentials
-
OpenCode. [3]
- Taken
- OpenAI, Anthropic and Google keys saved in its Console
- How
- An old system that was being retired
-
Railway. [1]
- Taken
- Customers' stored secrets, some decrypted
- How
- Not yet disclosed
-
HARD publishes its article, at High.
What it said to do thenIf your company, family office or anyone building software for you uses Railway, OpenCode or Fireworks AI, ask them to change every stored key and password today, and to set spending limits on AI accounts. -
Update 1 · Vendor revised
Railway says the attacker was inside its systems from 20 to 22 October, that stored keys and passwords in up to 1.85% of workspaces (about 100,000) may have been exposed, and that it can't yet rule out that customers' source code was read. On 26 October it said the incident was resolved for existing customers, but keys taken before then work until they're changed.[4]
What to do nowIf your company, family office or anyone building software for you uses Railway, OpenCode or Fireworks AI, ask them to change every stored key and password if they haven't yet, and to set spending limits on AI accounts. If they use Railway, also ask them to check their GitHub and database access logs, as Railway recommends. -
Update 2 · Wider attacks
Northflank, a platform that runs customers' apps and databases, said on 30 October that attackers got at the secrets customers store with it, and that customers should assume every one was decrypted. Several customers say their AI keys have already been used. Wiz, the security firm that raised the alarm, now counts nine AI developer platforms hit since 6 October, which it calls Black October, and says it has seen stolen keys tried within 30 minutes of being taken.[5][6]
What to do nowIf your company, family office or anyone building software for you uses Northflank, Railway, OpenCode, Fireworks AI or any similar platform, ask them to change every key and password stored there today, check their AI providers' usage and bills, and set spending limits on AI accounts.
Why AI keys
An AI key is a credit card for computing. Whoever holds it can run the most capable models in the world, as much as they like, on someone else's bill. When OpenCode's customers' keys were taken, TechCrunch reported unauthorised charges on their OpenAI, Anthropic and Google accounts, some in the hundreds of dollars and a few over a thousand.[3]
 OpenAI
 Anthropic
 Google
The bills are the visible part. Stolen access to frontier AI is useful for exactly the work we've been writing about: research on targets, convincing messages at scale, and finding weaknesses in software. The companies that sell AI watch their own customers closely. A stolen key lets someone borrow a customer's good name.
Every company you hand a key to becomes a place that key can be stolen from.
Why it's the platforms
None of these customers did anything wrong. Each made a sensible choice: store the key with a trusted platform, so their software can use it. That convenience means one platform ends up holding thousands of keys, which makes it the most efficient place to rob.
It's the same pattern as the target in our essay. The weak point usually isn't you. It's the accountant's software, the property manager's portal, the platform your developers picked. You can do everything right and still be exposed by someone you trusted with access. A reused password did the same to millions of families in the 23andMe breach.
How this reaches a family
- Keys stored with a platformWhoever builds software for you keeps its passwords and AI keys on Railway, OpenCode or Fireworks AI.
- The platform is breachedThe keys are copied, some of them decrypted.
- Someone else uses themAI bills run up in your name, and the data those keys open is read.
- HARDEngineerIn discovery, your engineer lists the accounts and services that hold the family’s keys and who looks after each. When one is breached, they make sure every key is changed, not just the obvious ones.See how it works
What to do
The steps below are from the article as first published, on 22 October 2026.
- Ask anyone who builds software for you. Your company, the family office, a startup you've backed. Do you use Railway, OpenCode or Fireworks AI? If so, have you changed every key and password stored there since the disclosures?
- Put a ceiling on every AI account. OpenAI, Anthropic and Google all let account owners set spending limits or budget alerts. A stolen key with a limit is an annoyance. Without one, it's an open tab.
- Check what's connected to your own accounts. Google, Microsoft and Apple each list the apps you've given access to. Remove anything you don't use. Each one holds a key to you.
- Ask your vendors one question. Where are our keys stored, and who can read them? A good answer is specific. A vague one tells you what you need to know.
Or have someone keep that list for you. Knowing which companies hold keys to your family, and checking on them when the next platform falls, is what private cybersecurity is for.
Related
Situations
- Binance robbed of US$6.3 billion in 20 minutes, the biggest crypto theft on record Data breach, high, 31 Oct 2026
- Scribd breached: account details, and for some card details, of Scribd, Everand, SlideShare and Fable users Data breach, watch, 31 Oct 2026
- Capcom confirms 11.7 million CAPCOM ID accounts were accessed Data breach, watch, 24 Oct 2026
- Hijacked at the registrar: crypto sites bought through Name.com and Vercel served a wallet drainer Scam, high, 1 Nov 2026
- Every situation, in the Situation Room
References
Checked against the sources. Where a company hasn't said something, neither have we.
- ^ Railway (). “Security disclosure: Wednesday October 21st”. Railway's own notice: secrets accessed, some decrypted, deployments paused, and its view that this is part of a series.
- ^ Fireworks AI. “October 2026 security incident”. Fireworks AI's bulletin: stolen internal credentials used to reach secrets in customers' evaluation jobs.
- ^ TechCrunch (). “Hackers hit AI coding tool OpenCode, running up charges on users' AI accounts”. 1.4% of Console users affected, charges on OpenAI, Anthropic and Google accounts, and how each provider responded.
- ^ Railway (). “Preliminary Report: Oct 21st Security Incident (updated 26 October)”.
- ^ Northflank (). “Security incident”.
- ^ Wiz (). “Black October” for AI developer platforms.
- Dealroom. “OpenCode breach drains users' AI keys as platforms holding customer credentials come under attack”. The wider pattern: platforms that hold customers' keys to other services.
Situation Room articles are updated as events develop: updates are added to the timeline, and never edited away. Follow them by email or RSS.