

The firewall and email gateway need fixing
Palo Alto firewall and Cisco email gateway flaws exploited; fixes available, US agency deadline 17 Oct
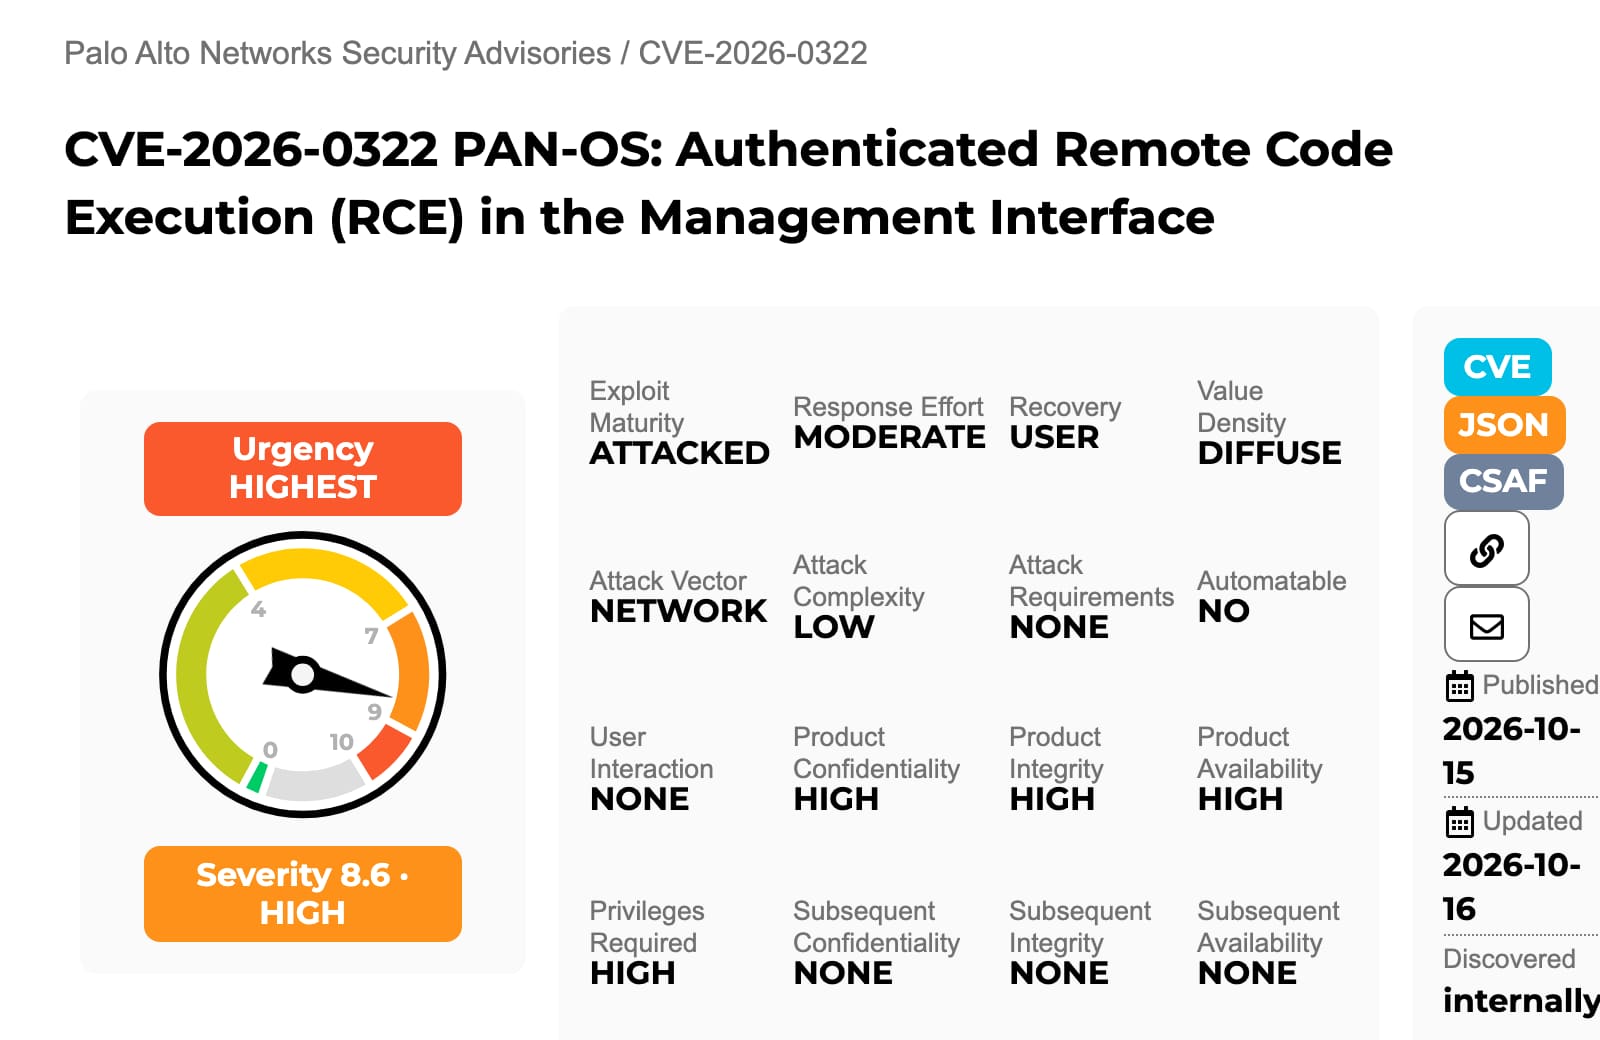
Palo Alto Networks reports very limited exploitation of its PAN-OS management interface, while Cisco confirms attacks against Secure Email Gateway. CISA added both flaws to its exploited-vulnerabilities catalogue on 14 October, with a 17 October remediation deadline for US federal civilian agencies.
What to do
- Get a written answer from your IT provider.Ask whether either product is in use, which devices are affected and which fixed versions are installed. Include any systems managed by an outside provider.
- Restrict firewall management access.Have the provider allow only trusted internal addresses while arranging the PAN-OS update. Treat this as risk reduction, not a substitute for patching.
- Check for an earlier break-in.Cisco warns that attackers can hide evidence on the gateway. Ask the provider to review independent network and firewall logs as well. If compromise is suspected, preserve evidence and follow Cisco’s recovery guidance before upgrading or rebuilding.
What happened
If your business or family office uses Palo Alto Networks firewalls or Cisco Secure Email Gateway, ask its IT provider for a patch check today. Both have flaws already being used in attacks. CISA added them to its exploited-vulnerabilities catalogue on 14 October[1].
Palo Alto describes the exploitation it has seen as very limited. Cisco also confirms active exploitation. These disclosures establish attacks against the products; they do not establish that your organisation has been breached.
- Palo Alto Networks
- High CVE-2026-0322: management access and a login required.
- Cisco
- Critical CVE-2026-76519: affects email processing; no attacker login required.
- Federal deadline
- 17 October 2026, for US federal civilian agencies.
The full story3 more sections
Who is affected
The PAN-OS flaw affects PA-Series and VM-Series firewalls and Panorama management systems. An attacker who can reach the management interface and authenticate can gain the device’s highest level of control. Cloud NGFW and Prisma Access are unaffected. Palo Alto’s advisory[2] recommends allowing management access only from trusted internal addresses.
Cisco’s flaw affects physical and virtual Secure Email Gateways running vulnerable software when File Reputation is enabled in a mail policy and Content Scanner Tools is older than 25.3.0.5525. It can give an attacker control of the gateway through email processing. Restricting its administration page does not address that route. Cisco explains the affected configurations[3].
Which fixes to check
PAN-OS fixes include 12.2.4, 12.1.10-h2, 11.1.16-h3 and 10.2.18-h12. Other maintenance releases have their own fixed versions, so your provider should match each device to the vendor’s table. For 11.2, fixed maintenance releases include 11.2.13-h3; 11.2.16 is expected on 15 October. The 14 October report[4] distinguishes available fixes from that pending release.
For Cisco, Content Scanner Tools 25.3.0.5525 or later supplies the fix on licensed, supported AsyncOS releases without a restart. Cisco also recommends moving releases older than 16.5 to AsyncOS 16.5.0-780. Ask for the installed scanner version, even if automatic updates are enabled.
What the deadline means
The 17 October deadline concerns US federal civilian agencies. CISA’s directive does not impose that deadline on an Australian business or family office, but the agency urges other organisations to prioritise exploited flaws too[1]. HARD’s advice is to act now.
Timeline
-
HARD publishes its article, at High.
After the news
- How to update every device phones, computers, browsers, TVs and routers
References6
- ^ CISA (). “CISA Adds Four Known Exploited Vulnerabilities to Catalog”. Official bulletin confirms both additions, evidence of exploitation and the directive’s federal scope.
- ^ Palo Alto Networks (). “PAN-OS: Authenticated Remote Code Execution in the Management Interface”. Affected products, authentication requirement, exploitation, fixes and mitigation; updated 15 October to record publication of 11.2.16.
- ^ Cisco (). “Cisco Secure Email Gateway Arbitrary File Write Vulnerability”. Affected configurations, active exploitation, scanner and AsyncOS fixes, and investigation and recovery guidance.
- ^ BleepingComputer (). “Palo Alto Networks warns of PAN-OS RCE flaw exploited in attacks”. Contemporaneous report confirms limited exploitation, federal deadline and 11.2.16 expected on 15 October.
- NIST (). “CVE-2026-76519 Detail”. Indexed NVD record reproduces Cisco’s description and the 14 October KEV addition and 17 October due date.
- Help Net Security (). “CISA flags exploited flaws in Palo Alto, Cisco and Ahsay products”. Requested report read for corroboration; postdates the draft’s dateline and supplies no unique claim to the story.
Situation Room articles are updated as events develop: updates are added to the timeline, and never edited away. Follow them by email or RSS.