

NIKKE PC launcher hacked to spread password-stealing malware; official security check released
Level Infinite confirms that tampered Windows launcher files could run malicious programs on players’ PCs. Analysis found remote-control and data-stealing capabilities, including an optional component targeting crypto wallets; successful cryptocurrency theft has not been established. The publisher says the current launcher is safe and provides an official security check.
Hackers used the game’s Windows launcher to distribute malware capable of remote control and data theft. Players need to check the computer and protect the accounts they used on it.
What happened
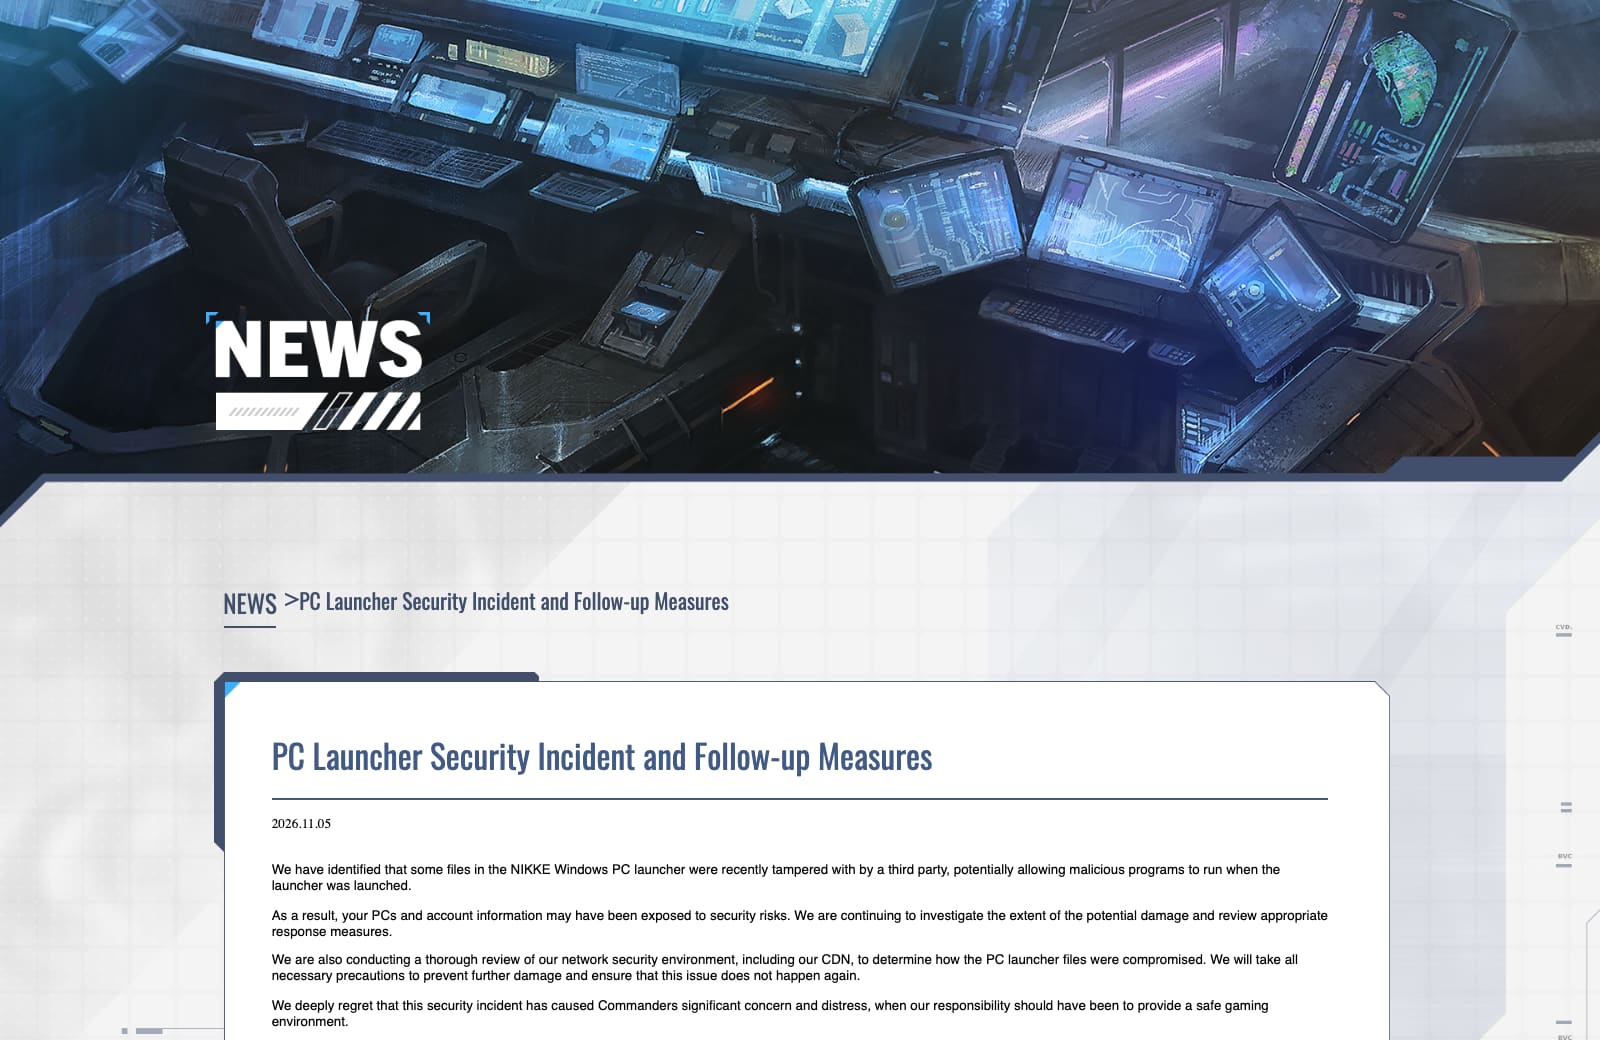
If someone in your household plays Goddess of Victory: NIKKE on a Windows PC, check when they last opened its launcher. Publisher Level Infinite confirms that attackers tampered with launcher files, potentially running malicious programs on players’ computers. Its instructions cover accounts used on the affected PC, beyond the game itself. NIKKE’s official announcements, reproduced here[1] confirm the incident.
The publisher’s timeline dates the tampering to 27 September and malware distribution to 30 October. Researcher MotherSphere reports evidence of the remote-control program running as early as 23 October. Those accounts differ, but both point to checking computers used since September. The publisher describes corrective work on 4 November. MotherSphere’s analysis[2] sets out the timing disagreement.
- HARD level
- High
- Who should check
- Anyone who opened the Windows launcher after 27 September, 15:41 (UTC+9).
- Mobile game
- Unaffected, according to NIKKE.
- Official malware check
- Available from 5 November, 08:00 (UTC+9).
Timeline
-
HARD publishes its article, at High.
Who is affected
NIKKE says people who played only the mobile version need no additional security measures for this incident. For a shared Windows computer, ask everyone who uses it whether they opened the launcher during the period covered by the notice. NIKKE’s manual-check notice[3] defines the affected group.
What the malware could take
MotherSphere’s analysis describes a program able to control the computer remotely, read files, capture screenshots and steal browser information. BleepingComputer independently examined an additional component with code targeting crypto wallet recovery phrases and private keys, including wallets such as MetaMask and Phantom. Its report could not establish whether that component was deployed or cryptocurrency was stolen. BleepingComputer’s investigation[4] distinguishes those capabilities from confirmed losses.
Level Infinite says the currently distributed launcher is safe to use. That statement concerns the launcher now; follow its recovery instructions for a PC that may already have been exposed. The reproduced publisher notices[5] include both automatic and manual checks.
What to do
- Use the official security check.Close all browsers, including Chrome, before launching the current official PC client. Agree to removal if its security check detects malware. If you have uninstalled the launcher or prefer a manual check, follow NIKKE’s separate guide; ask a trusted technician to help with it.
- Protect accounts from an unaffected device.Change passwords for accounts used on the affected PC. If you used or stored API keys or access tokens there, revoke and replace them too.
- Scan Windows as well.Update your antivirus and run a full scan. NIKKE also recommends Microsoft Defender Offline. Find it under Windows Security → Virus & threat protection → Scan options. Save your work first: Microsoft’s instructions[6] explain that the scan restarts the PC.
- Report suspected harm.Contact NIKKE’s official Customer Support if you believe you were affected or suffered a loss.
Related
Situations
- Google shuts down a botnet built into 1.3 million Android TV boxes, but the backdoor stays on them Malware, high, 4 Nov 2026
- Synology storage devices hit by ransomware; DSM updates available Software flaw, high, 6 Nov 2026
- DreamHost breach exposed file-transfer passwords; email and files may also have been accessed Data breach, high, 6 Nov 2026
- OpenSSH update blocks a login bypass on some musl Linux servers; Alpine packages available Other, high, 6 Nov 2026
- Every situation, in the Situation Room
References
- ^ NIKKE, reproduced by Sotwe. “NIKKE official account announcements, reproduced”. Official announcement text confirms tampering, the affected Windows audience, mobile exclusion and reporting route.
- ^ MotherSphere. “NIKKE PC launcher compromise: incident analysis”. First-hand malware analysis and reported evidence of execution on 23 October, earlier than the publisher’s distribution date.
- ^ Level Infinite / NIKKE (). “Manual Security Check Instructions for the PC Launcher”. Affected users, mobile exclusion and manual recovery guidance; text read in Nikke.gg’s reproduction.
- ^ BleepingComputer (). “NIKKE PC game launcher hacked to spread remote access, data-stealing malware”. Independent examination of malicious scripts and wallet-stealing component; successful crypto theft remains unestablished.
- ^ Nikke.gg, reproducing Level Infinite notices (). “Official Announcement: PC Launcher Security Incident, Manual Check, Follow-up & Apology”. Full reproduced publisher notices, including current-launcher safety statement, scanner and account-protection advice.
- ^ Microsoft. “Microsoft Defender Offline scan in Windows”. Windows Security navigation and the requirement to save work before the offline scan restarts the PC.
- Level Infinite / NIKKE (). “PC Launcher Security Incident and Follow-up Measures”. Publisher timeline and recovery instructions; text read in Nikke.gg’s reproduction because the original page did not render.
Situation Room articles are updated as events develop: updates are added to the timeline, and never edited away. Follow them by email or RSS.