

DigiCert breach exposed customer contact details, and some passports and driver’s licences
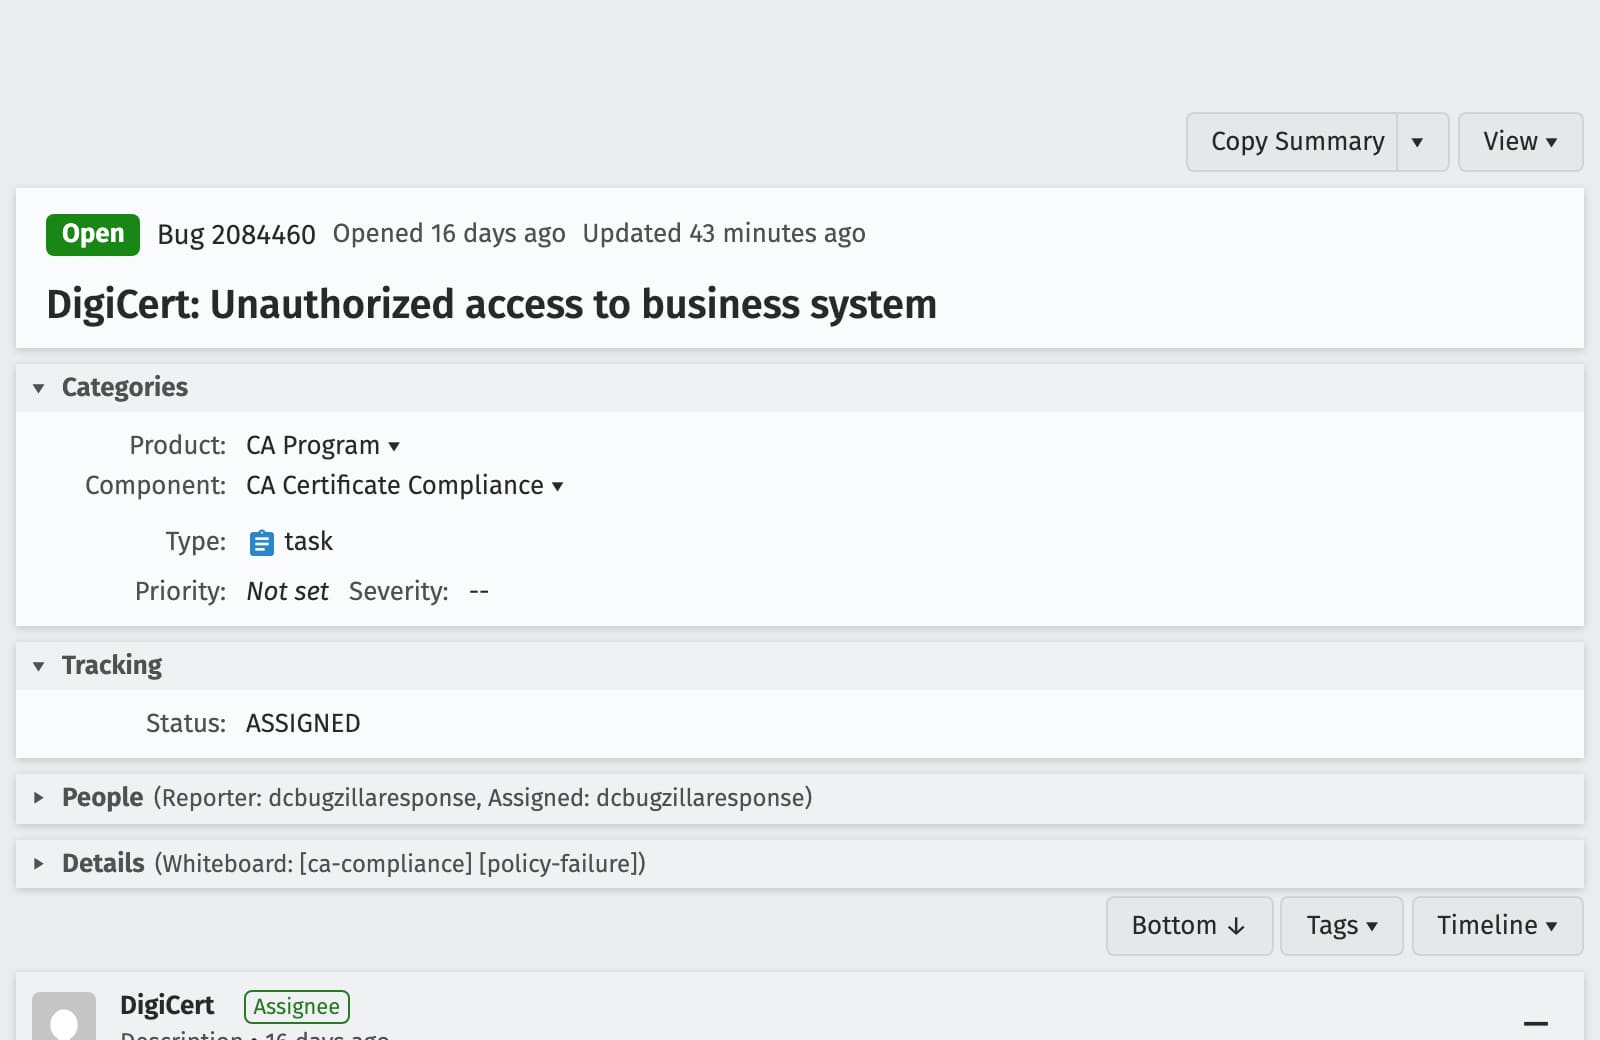
A February 2025 server move left a DigiCert business system open to the internet. Outsiders could create accounts there and read archived customer records: names, business emails, phones and addresses, and for a small minority a passport, licence or utility bill. DigiCert is still working out whose documents were involved.
An outsider read archived DigiCert customer records, a few with a passport, licence or utility bill attached. Certificates weren’t affected; watch for its notice and for convincing emails.
What happened
If you or your company has bought certificates from DigiCert, watch your inbox for its breach notice. An outsider read archived customer records held on one of its business systems, and a small number of those records included a passport, driver’s licence or utility bill a customer had provided.
DigiCert, which issues the certificates behind website padlocks and signed software, says the system was exposed to the internet by mistake during a February 2025 server move. Outsiders could create accounts on it, and a separate permissions flaw let those accounts read archived records. Its incident report[1] puts the reading between 27 June and 2 July 2026. DigiCert only confirmed that data had been accessed on 19 October.
- HARD level
- High for anyone who sent DigiCert an ID document
- Most records
- Names, business email addresses, phone numbers and business addresses
- Some records
- A driver’s licence, passport, utility bill or similar document
- Access
- 27 June to 2 July 2026; exposed since February 2025
- Not affected
- Certificates, logins and certificate services, DigiCert says
- How many
- Not disclosed
Timeline
-
HARD publishes its article, at High.
Who is affected
DigiCert is notifying business customers whose records were in the archive. It is still reviewing the identity documents to work out exactly whose were involved, and says it will tell those people once it knows, The Register reports[2]. It hasn’t said how many people that is.
The account that got in could only read. DigiCert says it could not change records, approve checks or issue certificates, and that certificates, customer logins and its CertCentral and DigiCert ONE services were not touched, according to BleepingComputer[3]. It told The Record[4] it has seen no evidence the information has been misused, and that it has reported the incident to law enforcement.
Why it took so long
DigiCert noticed the outside accounts in June but first concluded they couldn’t reach customer data. It fixed the flaw on 2 July without realising the archive had been read. Its report says the server move was treated as an infrastructure change, so it skipped a security review, and nothing alerted anyone to new accounts or unusual traffic.
What to do this week
- Find out whether you sent DigiCert an ID document.Ask whoever handles your company’s certificates whether a passport, licence or utility bill was ever sent to verify you. If DigiCert writes to say yours was involved, keep the letter.
- If your document was involved, guard against identity fraud.Ask the passport office or licensing agency that issued it whether it should be replaced. In the US, a credit freeze at Equifax, Experian and TransUnion is free; elsewhere, ask your bank and credit bureau about alerts.
- Expect convincing emails about certificates.Whoever read the archive knows names, phone numbers and that you buy certificates. Treat renewal, payment or verification requests as suspect until you’ve signed in to DigiCert yourself, by typing its address.
- You don’t need to replace certificates.DigiCert says no certificates were issued or changed. Reissue only if DigiCert tells you to.
Related
Situations
- Chainalysis says login details for all its users were exposed; customers should reset passwords and rotate API keys Data breach, high, 7 Nov 2026
- Gnosis Pay breach exposed details of its own-brand card customers; funds were not affected Data breach, high, 7 Nov 2026
- MetaMask’s staking service was breached; wallets, recovery phrases and keys were not Data breach, watch, 7 Nov 2026
- Ransomware takes down Queens Public Library’s website, app and Wi-Fi; patron data status unknown Data breach, watch, 7 Nov 2026
- Every situation, in the Situation Room
References
- ^ DigiCert, in Mozilla’s certificate authority incident tracker (). “DigiCert: Unauthorized access to business system”. DigiCert’s own incident report: the timeline, what the system held, the cause and the fixes.
- ^ The Register (). “DigiCert admits 16-month security lapse exposed customer information”. The notification email sent to customers, and the review of identity documents still under way.
- ^ BleepingComputer (). “DigiCert data breach exposes customer information, identity documents”. The customer notice’s wording on identity documents, and what DigiCert says was not affected.
- ^ The Record (). “Certificate authority DigiCert reports data breach involving business customer info”. DigiCert’s statements on misuse and law enforcement; the number affected is undisclosed.
Situation Room articles are updated as events develop: updates are added to the timeline, and never edited away. Follow them by email or RSS.