

Gnosis Pay breach exposed details of its own-brand card customers; funds were not affected
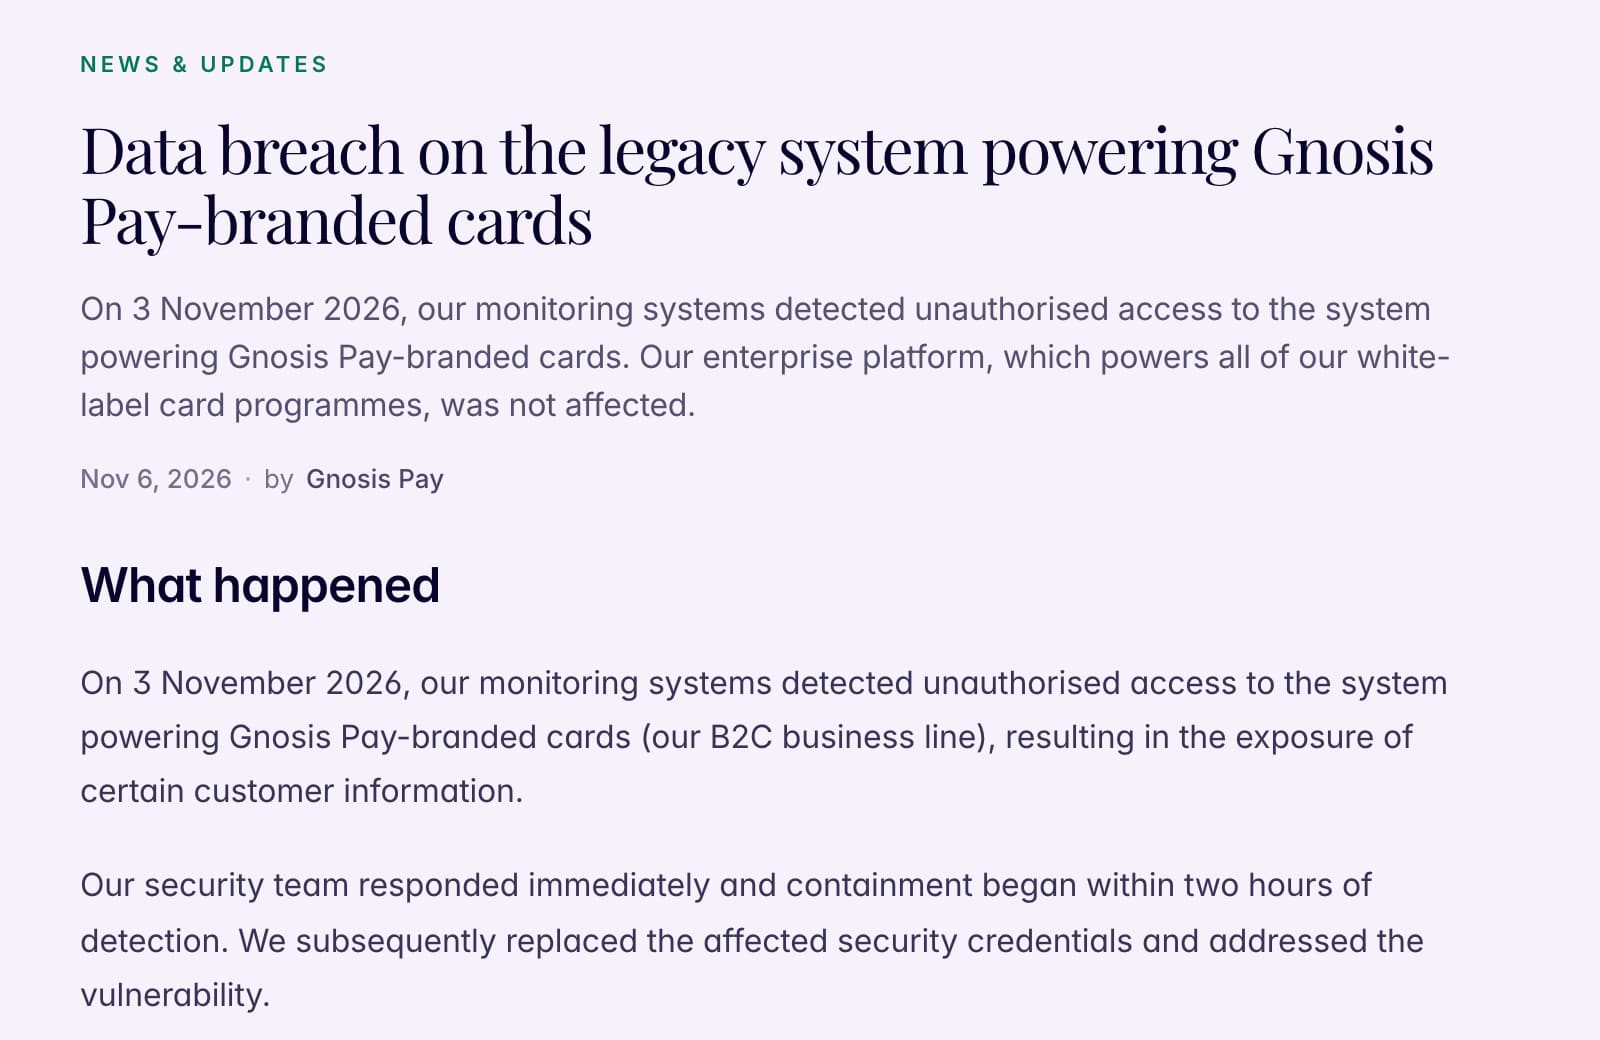
On 3 November Gnosis Pay found someone in the older system behind its own-brand cards. The company says it contained it within two hours, and that funds and partner-app cards weren’t affected. It hasn’t said publicly how many people or which details. Online payments now need 3D Secure until 20 December.
On 3 November Gnosis Pay found someone in the system behind its own-brand crypto debit cards. Funds weren’t touched, but cardholders should read their email and expect targeted scams.
What happened
If you have a Gnosis Pay-branded card, the crypto debit card, read the email Gnosis Pay sent on 6 November: it lists exactly which of your details were taken. On 3 November Gnosis Pay detected someone in the system behind those cards. Gnosis Pay says customers’ funds were not affected.
Its notice[1] says the company contained the break-in within two hours of spotting it, replaced the credentials that were compromised and fixed the weakness used. It has not said publicly how many customers are affected or which kinds of information were exposed, only “certain customer information”. That is why the email matters.
- HARD level
- High for Gnosis Pay cardholders
- Found
- 3 November 2026, contained within two hours
- Affected
- Customers of Gnosis Pay’s own cards; cards from partner apps were not
- Exposed
- Customer information, listed in each customer’s email; not public
- Funds
- Not affected, the company says
- Change
- 3D Secure required for online payments until 20 December
Timeline
-
HARD publishes its article, at High.
Who is affected
The breach was in Gnosis Pay’s older system for its own-brand cards, which it plans to retire on 20 December 2026. The separate platform that runs cards issued through partner apps was not affected, the company says. It has emailed every affected customer, reported the breach to its partners and the card issuer, and is in touch with data protection authorities. Neither The Block[2] nor the company gives a number.
This is a different incident from June’s, when an attacker took funds through a flaw in Gnosis Pay’s wallet setup and the company covered the losses[3].
Knowing who holds crypto, and where they live, is what makes the next scam convincing.
What to do this week
- Read Gnosis Pay’s email to you.It lists what was taken from your account. Follow any extra steps it recommends for that data. If you can’t find it, write to [email protected].
- Treat every message about your card as suspect.Gnosis Pay warns that scams may quote your real details or a real purchase. Don’t click links, don’t “re-verify” your identity, and never move funds because of an email, text or call.
- Never give out your recovery phrase, keys, PIN or card number.Gnosis Pay and its partner apps will never ask for them. Make any changes only in the official Gnosis Pay web app or your partner app, opened yourself.
- Approve only payments you started.Online payments now ask for a 3D Secure check[4] until 20 December. A prompt you didn’t expect means someone else is trying your card.
- Keep your address and holdings to yourself.The company asks customers to be careful who learns their address or how much crypto they hold, online or offline. Check your card transactions too.
Related
Situations
- Chainalysis says login details for all its users were exposed; customers should reset passwords and rotate API keys Data breach, high, 7 Nov 2026
- DigiCert breach exposed customer contact details, and some passports and driver’s licences Data breach, high, 7 Nov 2026
- MetaMask’s staking service was breached; wallets, recovery phrases and keys were not Data breach, watch, 7 Nov 2026
- Ransomware takes down Queens Public Library’s website, app and Wi-Fi; patron data status unknown Data breach, watch, 7 Nov 2026
- Every situation, in the Situation Room
References
- ^ Gnosis Pay (). “Data breach on the legacy system powering Gnosis Pay-branded cards”. The company’s notice: when it was found, what was and wasn’t affected, the 3D Secure change and what customers should do.
- ^ The Block (). “Gnosis Pay data breach exposes customer info; funds unaffected”. Reports the same scope; the number affected and the data involved are not disclosed.
- ^ Gnosis Pay (). “Post-mortem: Gnosis Pay vulnerability exploit”. The earlier, separate incident in June 2026.
- ^ Gnosis Pay. “Making secure online payments with 3D Secure”. How the extra check on online payments works.
- The Defiant (). “Gnosis Pay Confirms Breach of Consumer-Card System”. Secondary reporting, read against the notice.
Situation Room articles are updated as events develop: updates are added to the timeline, and never edited away. Follow them by email or RSS.