

Legoland Korea breach: annual-pass barcodes among data accessed
Legoland Korea says annual-pass customer records, including barcode numbers, were accessed
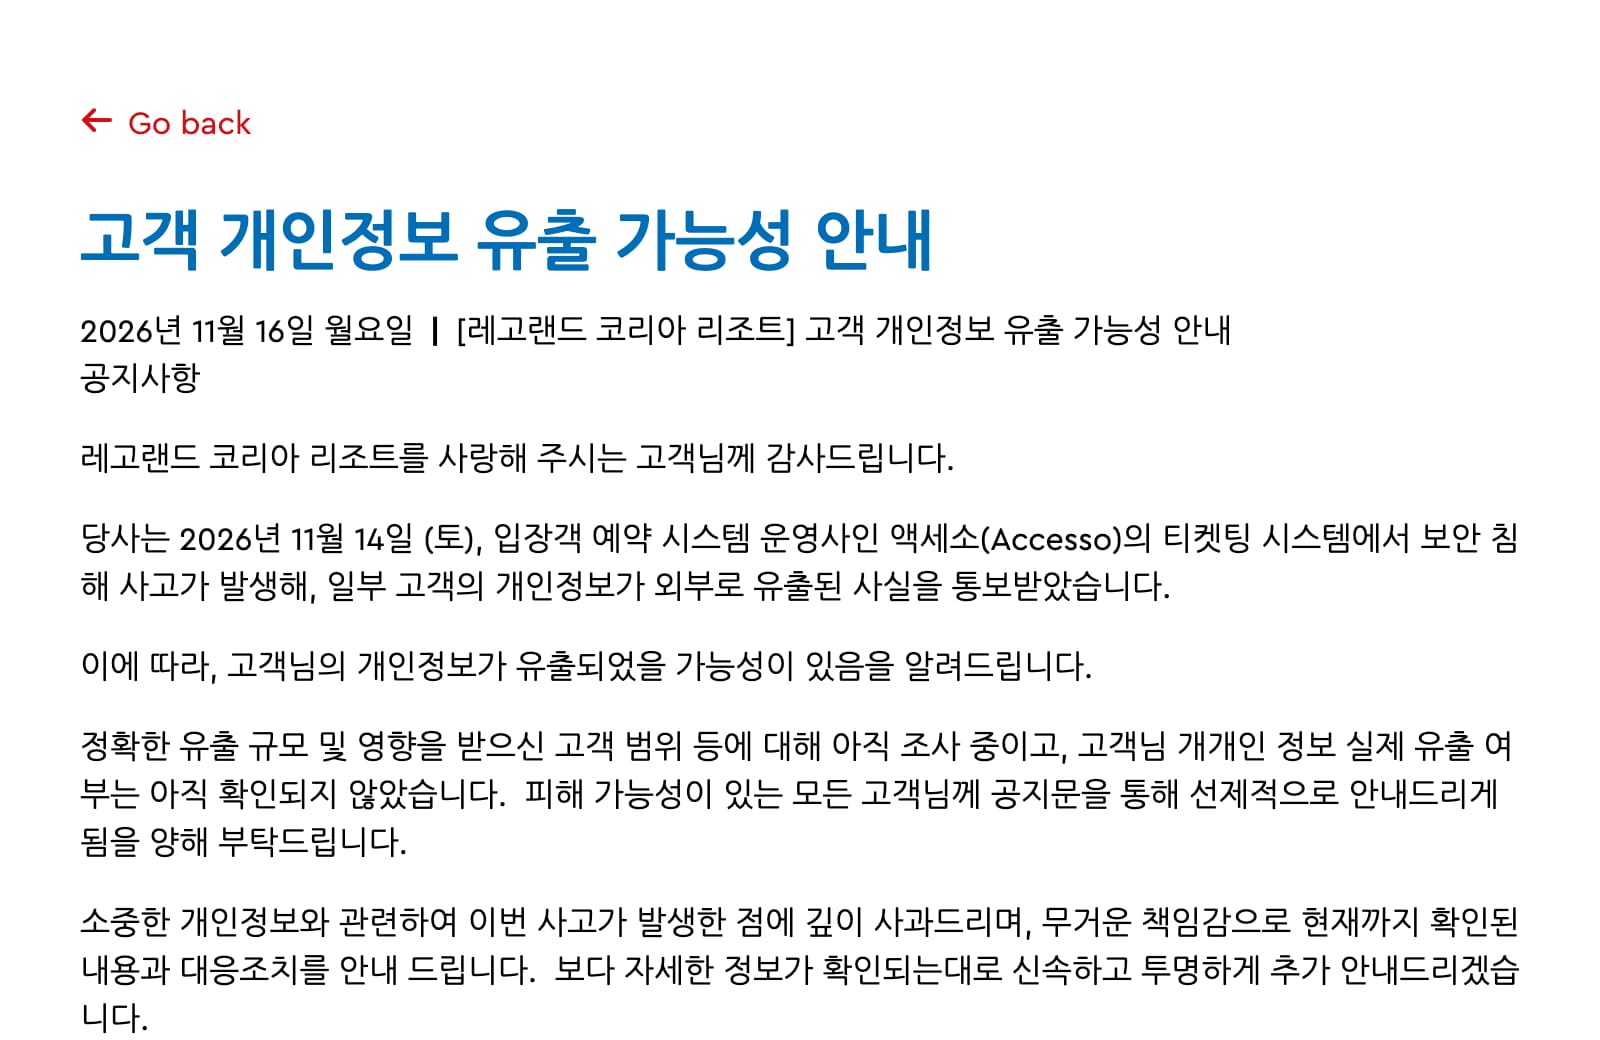
The records included names, addresses, email addresses, phone numbers, encrypted dates of birth and annual-pass barcode numbers. The number of affected customers remains under investigation, and Legoland says it has found no evidence of credit card or bank account information being exposed.
What to do
- Check the official notice.Open Legoland Korea's website yourself and check any notice sent to your family against it.
- Ask about each family member's pass.Request confirmation of which records were affected and whether the old barcode should be cancelled and replaced. The park lists privacy_notice@legoland.com for incident enquiries.
- Verify unexpected contact.The park warns about impersonation by email, text and phone. Do not follow unfamiliar links or provide personal details, verification codes or financial information before checking through official customer service. These precautions appear in its customer advice[3].
What happened
This concerns annual-pass holders at Legoland Korea Resort in South Korea only. Nothing in the notice points to any other Legoland park. If your family has annual passes for Legoland Korea Resort, check the park's breach notice. An unauthorised outsider accessed customer records through Accesso, its ticketing provider. The information viewed includes annual-pass barcode numbers alongside personal details, according to Maeil Business Newspaper's report[1].
Legoland's notice is dated 16 November. It says the park was informed on 14 November, with the actual incident date still under investigation. ChosunBiz places the unauthorised access on 14 November[2]; the park's own account does not establish that date.
- Information involved
- Names, addresses, email addresses, phone numbers, encrypted dates of birth and pass barcode numbers
- Customer count
- Still being investigated
- Payment details
- Legoland says no evidence of credit card or bank account exposure has been found
The full story2 more sections
Who is affected
The notice concerns some Korea Resort annual-pass customers. It says the scale is still under investigation and that it is not yet confirmed whether any individual's data actually leaked. It does not establish that every recipient's information was exposed or that customers at other Legoland parks are affected. The notice says Accesso removed the vulnerable access point, blocked the related source addresses and strengthened its security rules. That is the company's account, not an independent security assessment. Read the park's notice[3].
The barcode question remains open
The notice gives no barcode replacement instructions and does not establish whether an exposed number could be used by someone else. Ask the park what protection your pass needs before your next visit. Do not assume replacement is either required or unnecessary.
Timeline
-
HARD publishes its article, at High.
After the news
- Every data breach who was hacked, and how to check if you’re in one
- Data breach settlements the claims open now, by deadline
References3
- ^ Maeil Business Newspaper (). “Legoland Korea customer information exposed through reservation system”. Reports the six data categories, annual-pass scope, customer notifications and absence of evidence of payment-data exposure.
- ^ ChosunBiz (). “Legoland says hacker accessed reservation system and leaked customer data”. Reports access through Accesso and containment; places access on 14 November, unlike the primary notice's unresolved incident timing.
- ^ LEGOLAND Korea Resort (). “Customer personal information exposure notice [Korean]”. Primary notice: scope, notification date, data categories, reported containment, unresolved questions and customer contact.
Situation Room articles are updated as events develop: updates are added to the timeline, and never edited away. Follow them by email or RSS.