

A hijacked script took millions from Polymarket traders
Hijacked website script drains about US$2.7 million from Polymarket traders; refunds promised
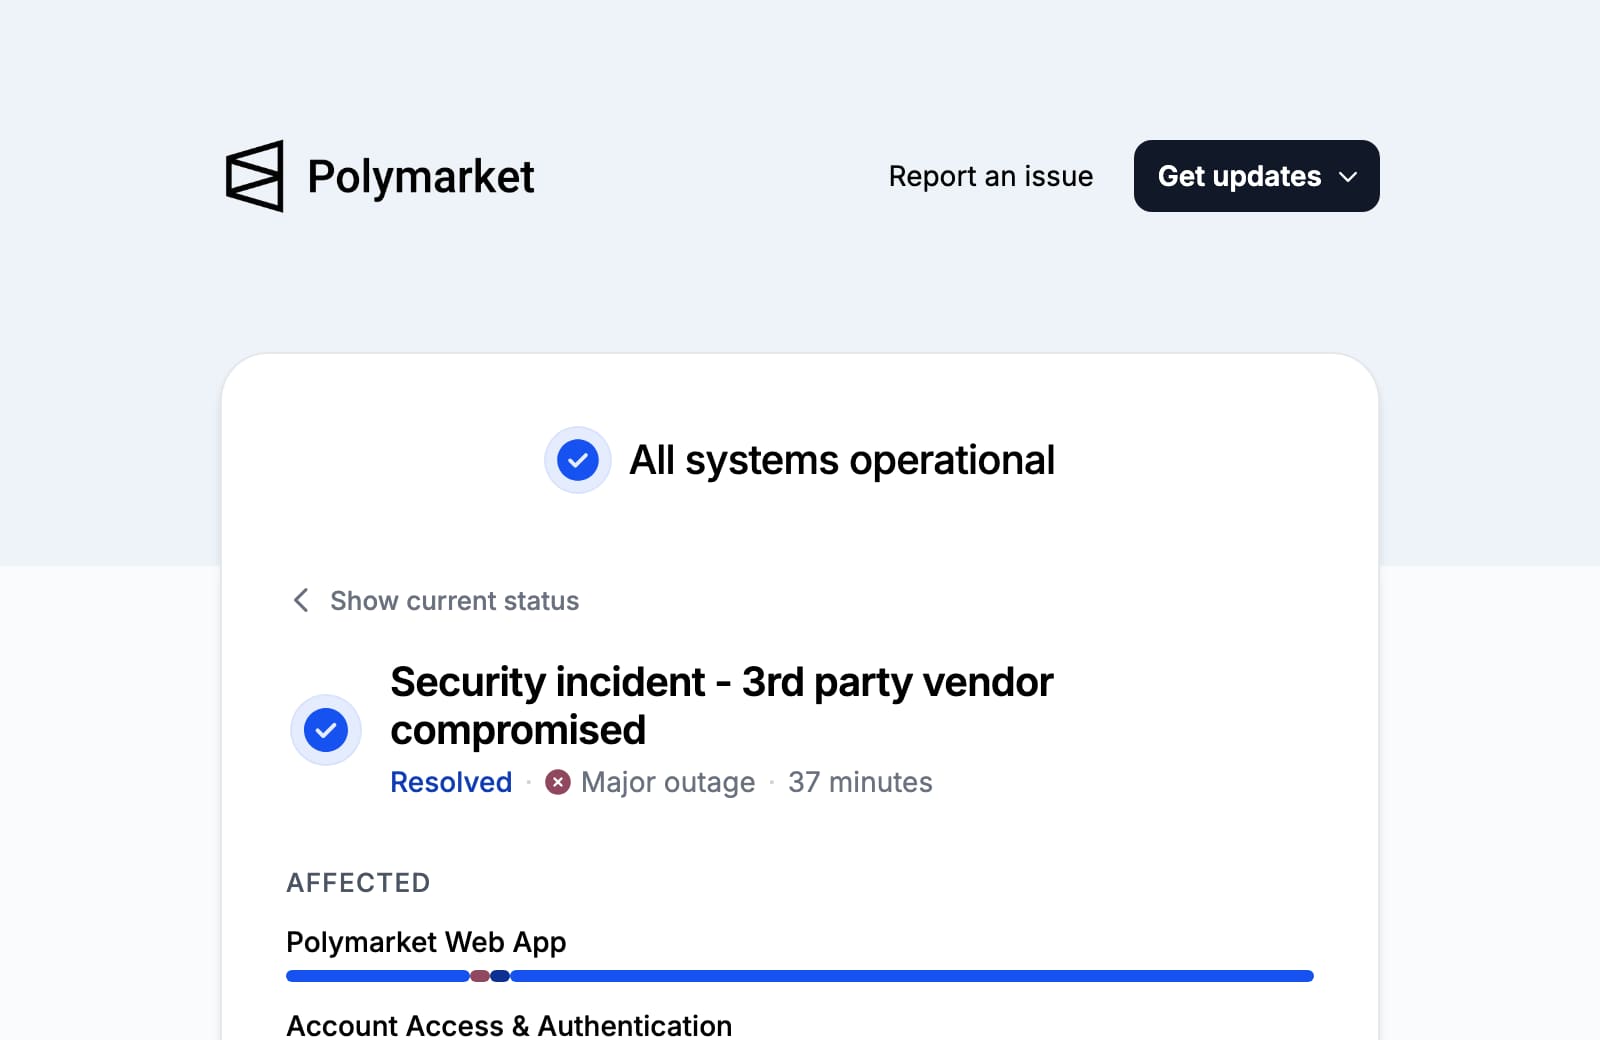
A compromised supplier’s website script targeted some users of Polymarket’s international platform on 29 October, using their open sessions to sell positions and transfer funds. Reports put losses at about US$2.7 million. Polymarket says it has fixed the issue, restored trading and pledged full reimbursement.
What to do
- Review your account activity.Check positions, completed sales, open orders and transfers around 29 October. Flag anything you did not authorise, including positions that disappeared.
- Keep a record.Save screenshots, transaction references, amounts and times before making changes. Keep your correspondence with support alongside them.
- Follow the official reimbursement updates.Open Polymarket’s status page directly. For account questions, use the website chat listed in its official support guide[5]. Ask whether your account is affected and how your losses will be assessed.
- Keep control of your wallet.Avoid unsolicited refund links and reject transaction requests you do not understand. Never give anyone your recovery phrase, private key or login code. Polymarket says it will never ask for your private key[6], and warns against sharing login codes even with staff[7].
What happened
Polymarket traders should check for sales and transfers they did not authorise after malicious website code targeted their accounts on 29 October. Reports put the loss at about US$2.7 million. The incident affected the international trading platform, Polymarket.com.
Polymarket temporarily blocked trading while it investigated. Customers could cancel existing orders, but new orders and trades would not go through. The company later said it had fixed the issue, reopened trading and promised to reimburse affected traders fully, according to The Block’s updated report[1].
- Severity
- High Unauthorised sales and transfers
- Incident date
- 29 October 2026
- Estimated loss
- About US$2.7 million; the total remains provisional
- Trading
- Restored, according to Polymarket
- Reimbursement
- Full repayment promised to affected traders
The full story3 more sections
Who is affected
The company’s incident record[2] says a supplier’s script was replaced with malicious code. It used some customers’ signed-in sessions to sell positions and move funds while they had the site open during a short window. That describes a subset of users, not everyone with a Polymarket account.
If you trade there, check both the positions you still hold and your recent activity. If a family member or adviser manages the account, ask them to review it with you and identify any unexplained changes.
The supplier behind the website
Reuters identified the supplier as DebugBear[3], citing a person familiar with the incident. DebugBear provides tools for monitoring website performance. It separately acknowledged a security incident and told customers using its website monitoring code to remove it. Polymarket’s initial statement described a compromised provider without naming it.
Why the loss total is provisional
The Block reported about US$2.65 million in a suspected attacker’s wallet, citing Arkham’s blockchain data. The Defiant reported[4] that investigator Bubblemaps traced roughly US$2.7 million moving out of Polymarket.
A larger US$3.46 million tally from Bubblemaps included US$750,000 attributed to a trader known as Car. He said he had moved about US$700,000 to a friend to protect it. That dispute leaves part of the larger tally unresolved. The Defiant reported that Polymarket had not yet supplied its own loss total or a reimbursement timetable.
Timeline
-
HARD publishes its article, at High.
After the news
- Every data breach who was hacked, and how to check if you’re in one
- Data breach settlements the claims open now, by deadline
References9
- ^ The Block (). “Polymarket resumes trading after $2.65 million exploit, says third-party provider was compromised”. Establishes the trading restrictions, subsequent reopening, reimbursement pledge and Arkham-based US$2.65 million estimate.
- ^ Polymarket (). “Security incident - 3rd party vendor compromised”. The update labelled 29 October describes the replaced script and affected open sessions; the separate 30 October postmortem is excluded.
- ^ Reuters via StreetInsider (). “Polymarket resumes trading after third-party security breach, to reimburse users”. Reports restoration, reimbursement pledge, DebugBear identification by a source and its code-removal warning.
- ^ The Defiant (). “Bubblemaps Traces $2.7 Million Outflow From Polymarket Breach”. Reports the US$2.7 million outflow, disputed larger tally and absence of a company loss total or repayment timetable; full text read in syndication.
- ^ Polymarket (). “How Do I Contact Support?”. Confirms official website chat and email support routes.
- ^ Polymarket (). “How Do I Export My Key?”. States that Polymarket will never ask for a user's private key.
- ^ Polymarket (). “How to Sign-Up”. Warns users never to share login codes, including with Polymarket staff.
- The Defiant via Crypto News (). “Bubblemaps Traces $2.7 Million Outflow From Polymarket Breach — syndicated full text”. Accessible full text of The Defiant's report, including Car's account that some funds were moved to safety.
- DefiLlama (). “Polymarket International: US$2.7M stolen”. The indexed database entry identifies the international platform, incident date and US$2.7 million estimate.
Situation Room articles are updated as events develop: updates are added to the timeline, and never edited away. Follow them by email or RSS.